
Attack Surface Monitoring (ASM)
Vulnerability Management

Breach and Attack Simulation (BAS)
Automated Red Teaming

EDR, SIEM, SOAR, Deception, AMTD, UEBA

CNAPP - CSPM, CWP, CIEM, Cloud ASM
Container Security

Automated Moving Target Defense (AMTD)
Network Deception
NAC
NDR

CPS Protection
OT IDS
Zero-Trust Access
OT Firewall

GRC Management
GRC Engineering
AI-Powered Risk Management


No integration headaches. One pane of glass. Single security data format. One platform.
Analyze and validate your infrastructure and security using adversarial thinking. Fix everything – from errors to exposures.
Minimize blast radius by stopping threat actors in their tracks. Strengthen security with pre-emptive guidance and cross-domain threat coverage.


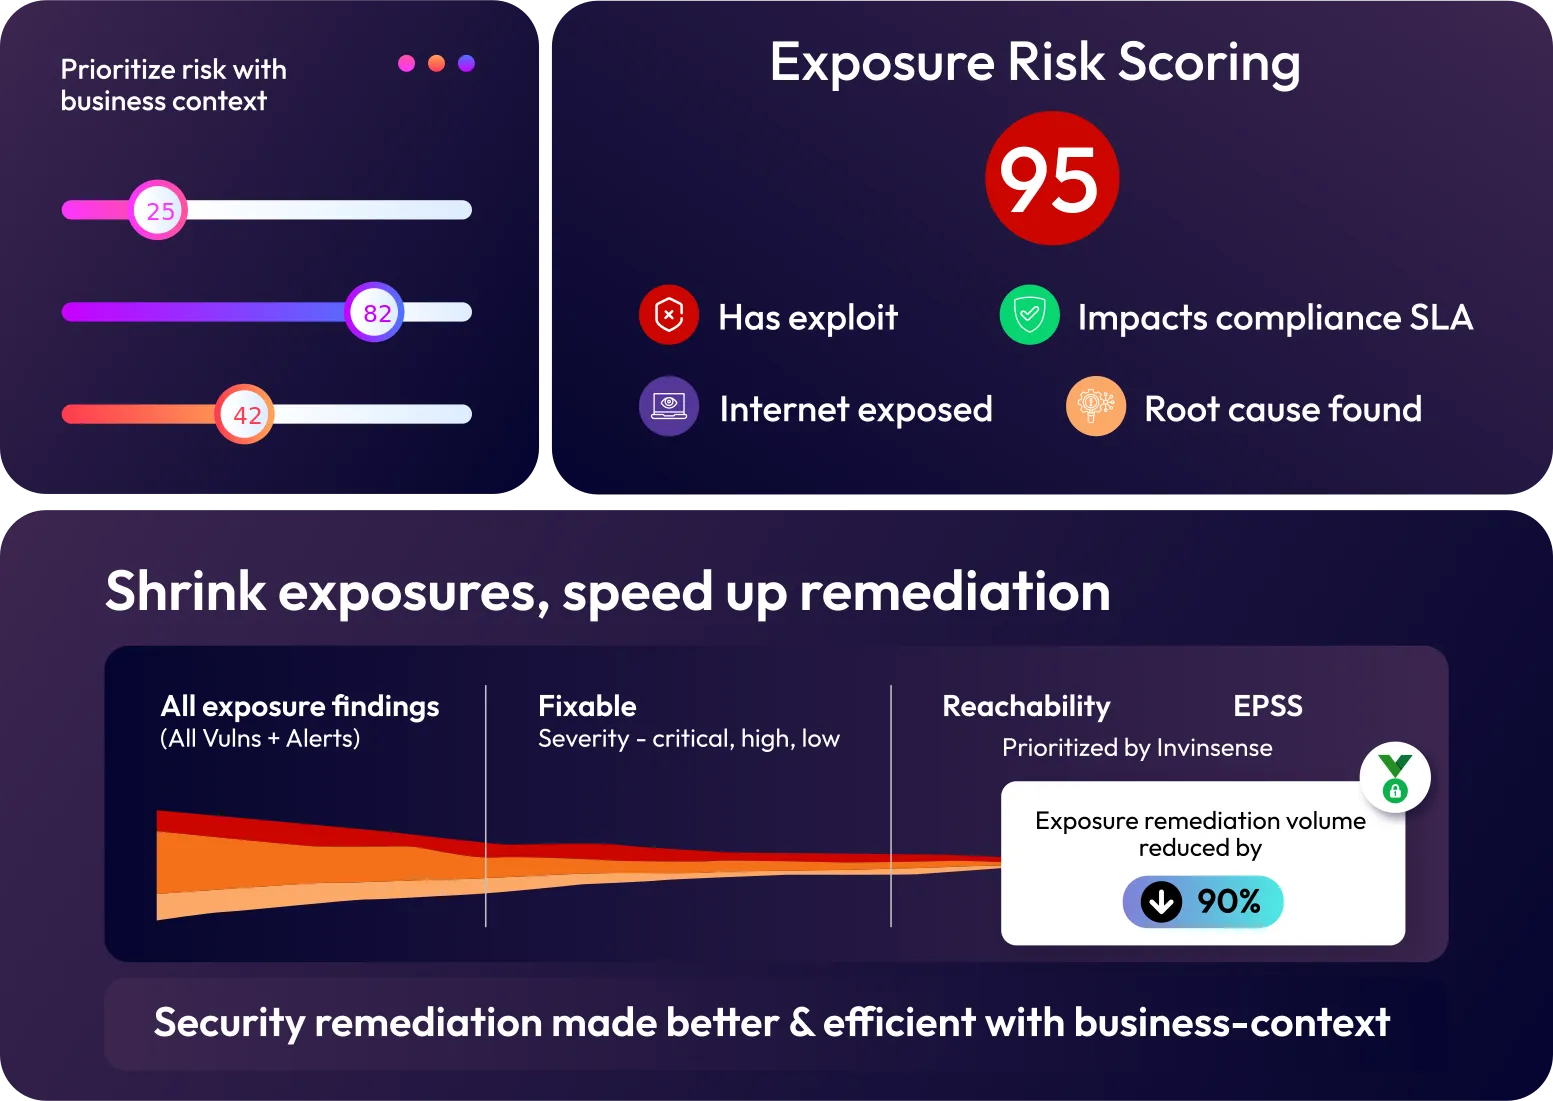
With Invinsense, we do not stop at detecting and prioritizing vulnerabilities and risks or threat detection, investigation, and response. We finish the job, get in the hustle and deliver business-context aware fixes.

The latest AI advances we add to Invinsense enhance all aspects of security – threat detection, deception, patching, threat simulation, red teaming, and security posture for compliance.
Utilizing expert human analysis and artificial intelligence, we help narrow thousands of alerts and exposure findings down to a few fixes that matter most. And we do this fast!

Invinsense gives security practitioners all the tools they need to end exposures and stop breaches. Get the big picture with deep visibility and context on invisible adversaries, unknown attack paths, and sneaky threats, to pre-empt modern attacks and outwit them early on.


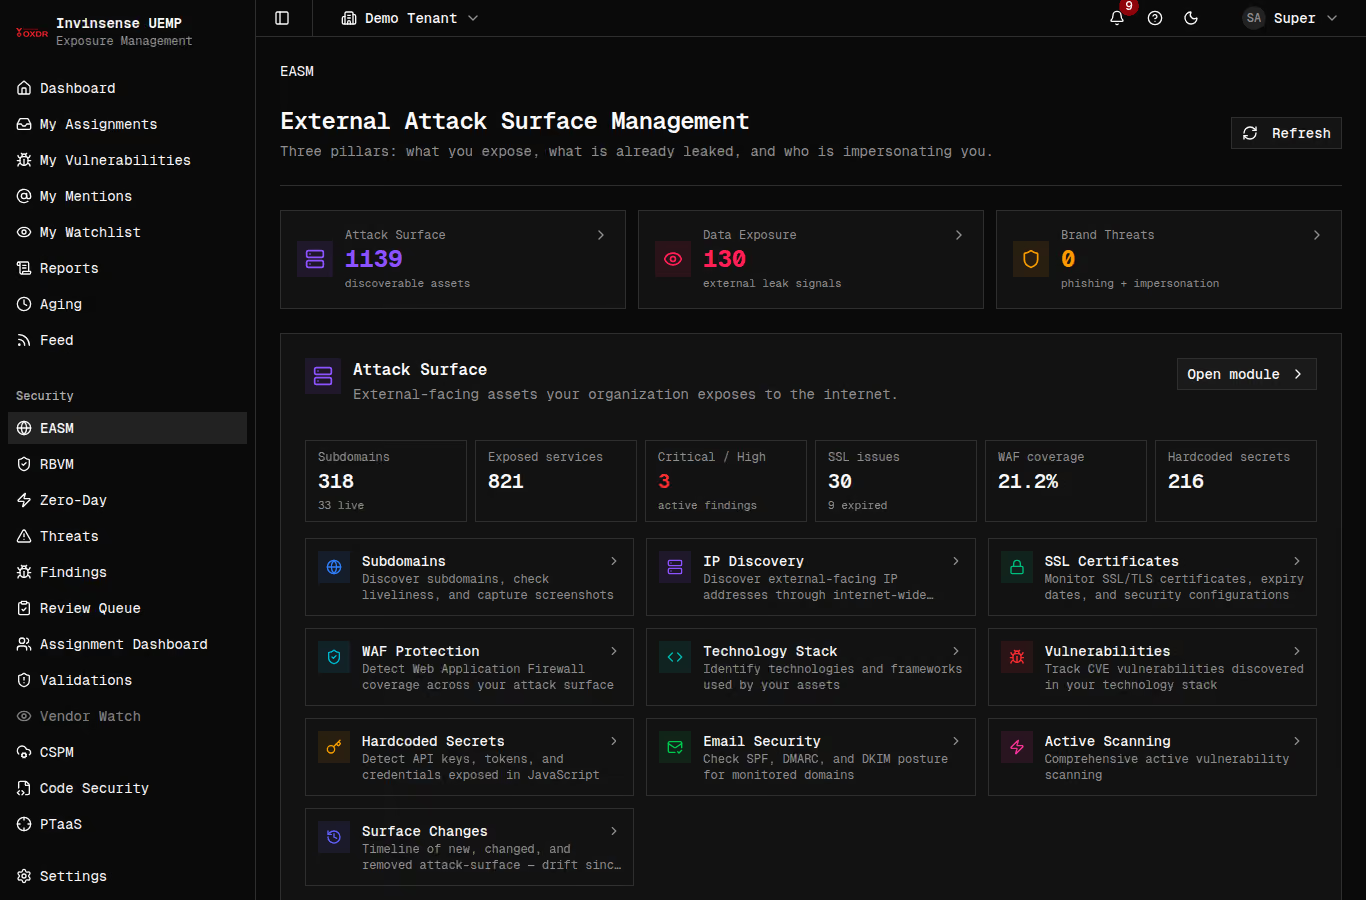
Continuously scans your organization’s digital environment, including data on the surface web as well as the dark web, to identify potential vulnerabilities and exposures. By mapping out all the assets, including networks, applications, and devices, it provides a comprehensive view of the potential entry points, which attackers might exploit.
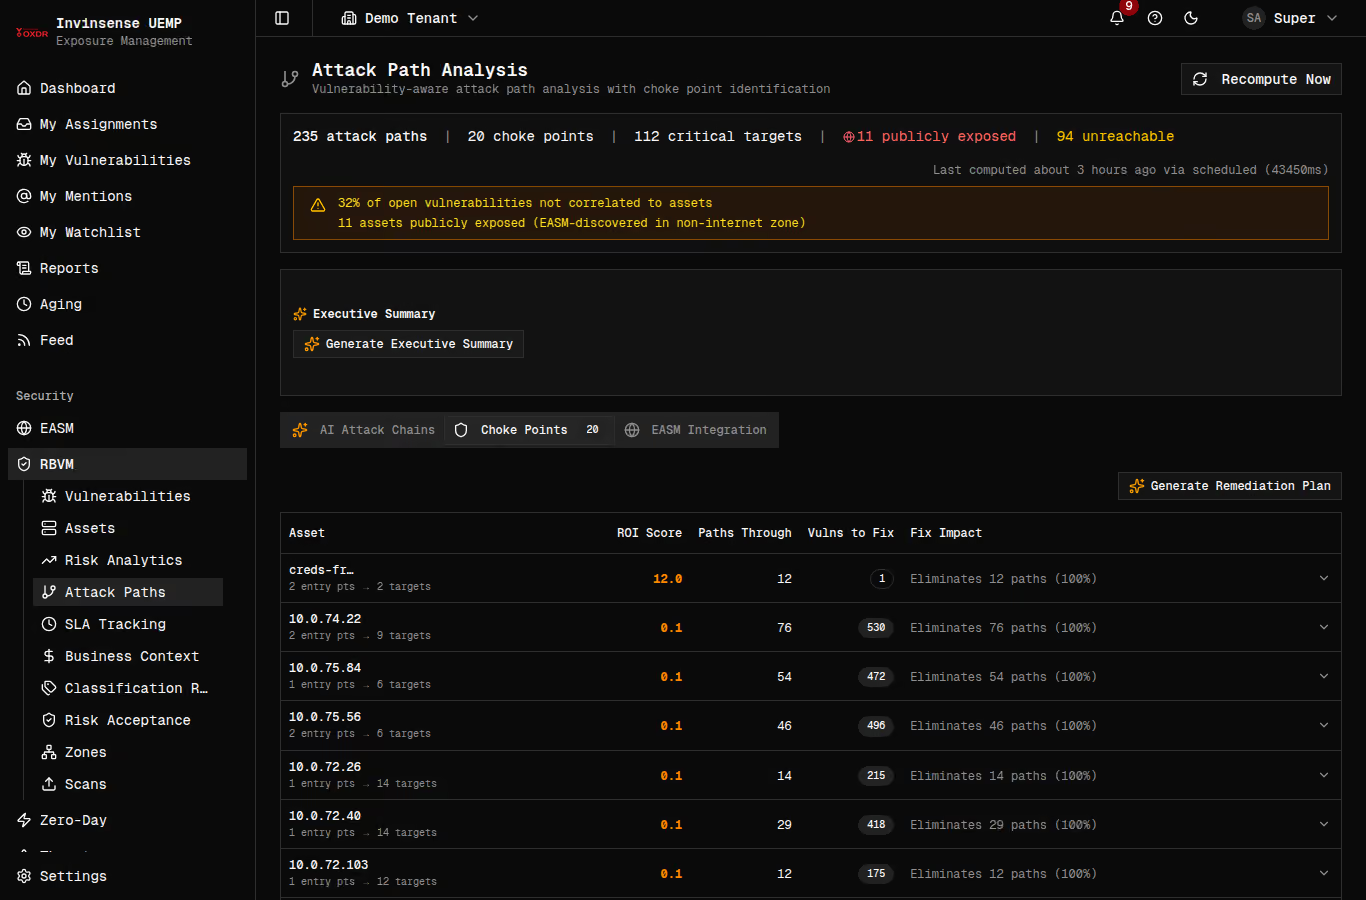
The module consolidates DevSecOps, security orchestration and full lifecycle vulnerability management capabilities. It helps ingest vulnerability and threat exposure information from a variety of sources, enablinga centralised vulnerability management and exposure assessment solution that gathers, stores and analyses thousands of vulnerabilities in one place. Additionally, the module also allows managing application security program, maintain productand application information, triage vulnerabilities and push findings to popular enterprise service management and workflow automation systems such as JIRA and Slack.
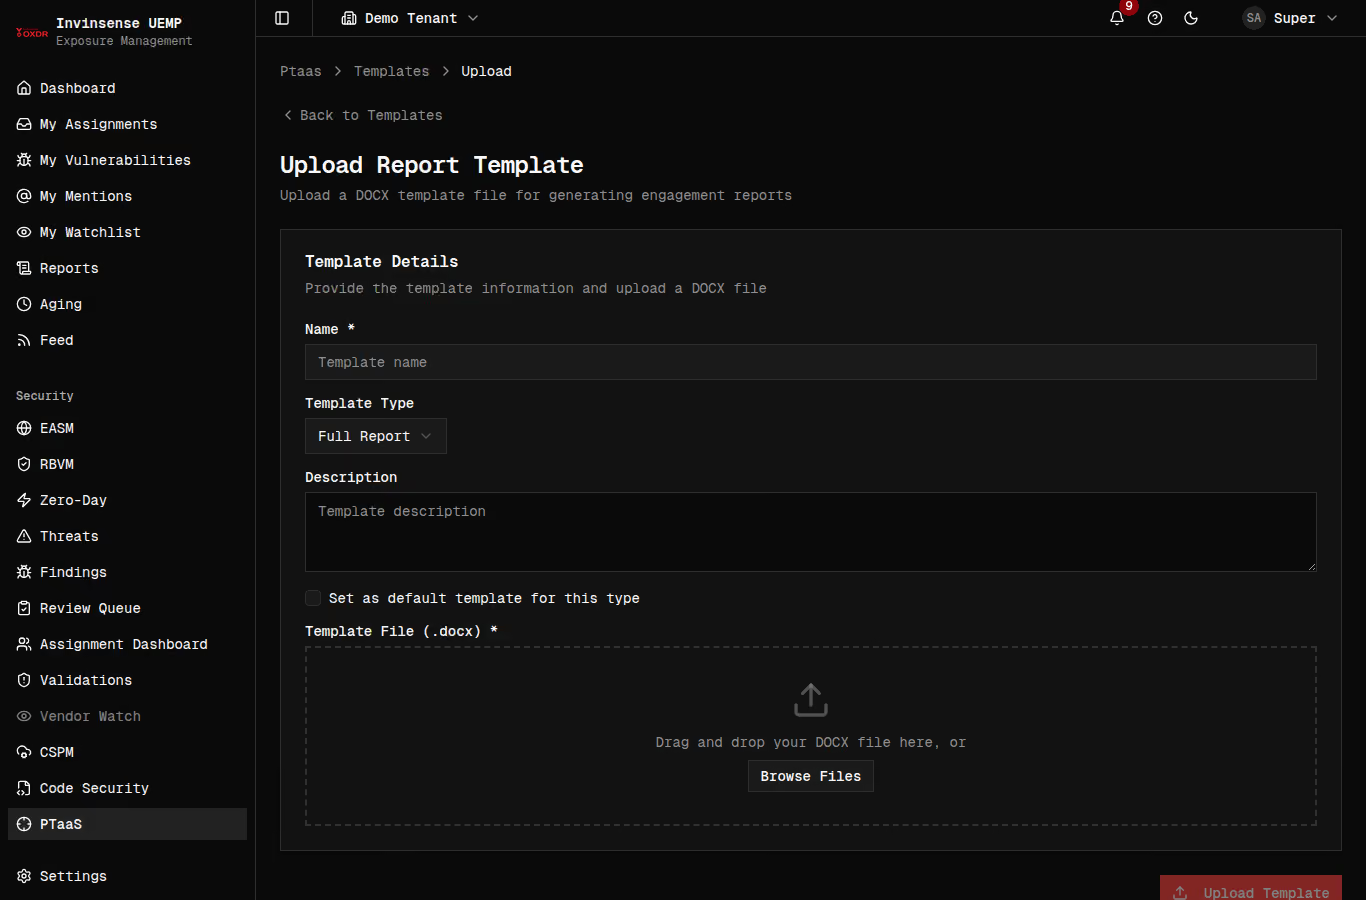
The Invinsense PTaaS module streamlines offensive security by allowing users to seamlessly initiate tailored penetration testing engagements across Web Application, Network, and Cloud environments. Practitioners can efficiently manage discovered threats using a centralized findings dashboard alongside a robust vulnerability library equipped with reusable templates for standardized documentation. Furthermore, the platform facilitates customized deliverable generation by allowing teams to upload personalized .docx report templates for their security engagements.
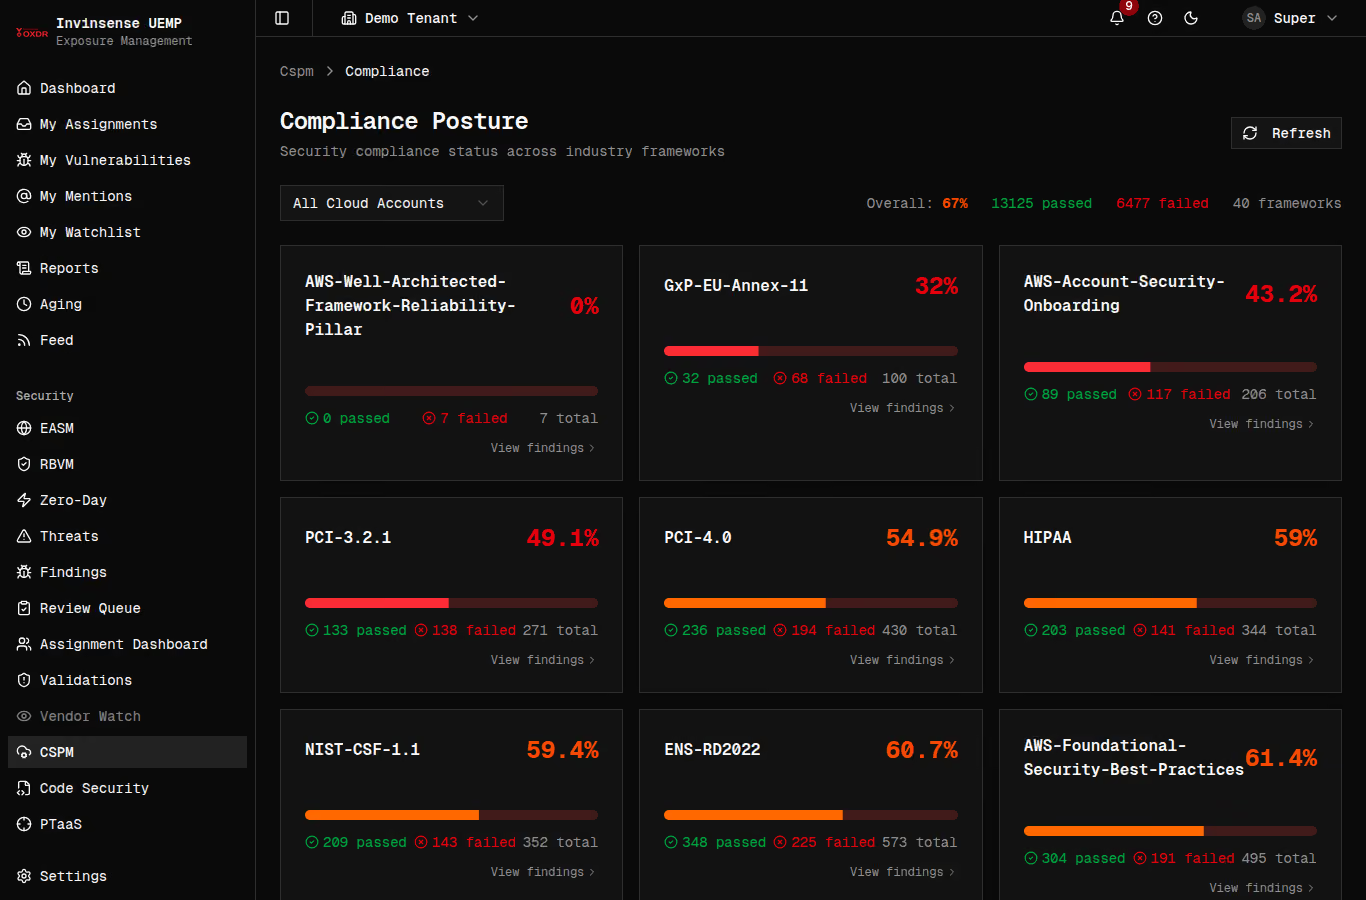
The Invinsense Cloud Security Posture Management (CSPM) module provides comprehensive visibility into cloud infrastructure security across AWS, Azure, and GCP environments. It continuously monitors cloud assets to rapidly identify and detail critical security misconfigurations, such as exposed ports, expired API keys, or identity and access management (IAM) gaps. By centralizing these security findings and calculating overall compliance rates, the module empowers practitioners to proactively harden their cloud architecture and efficiently remediate policy violations.
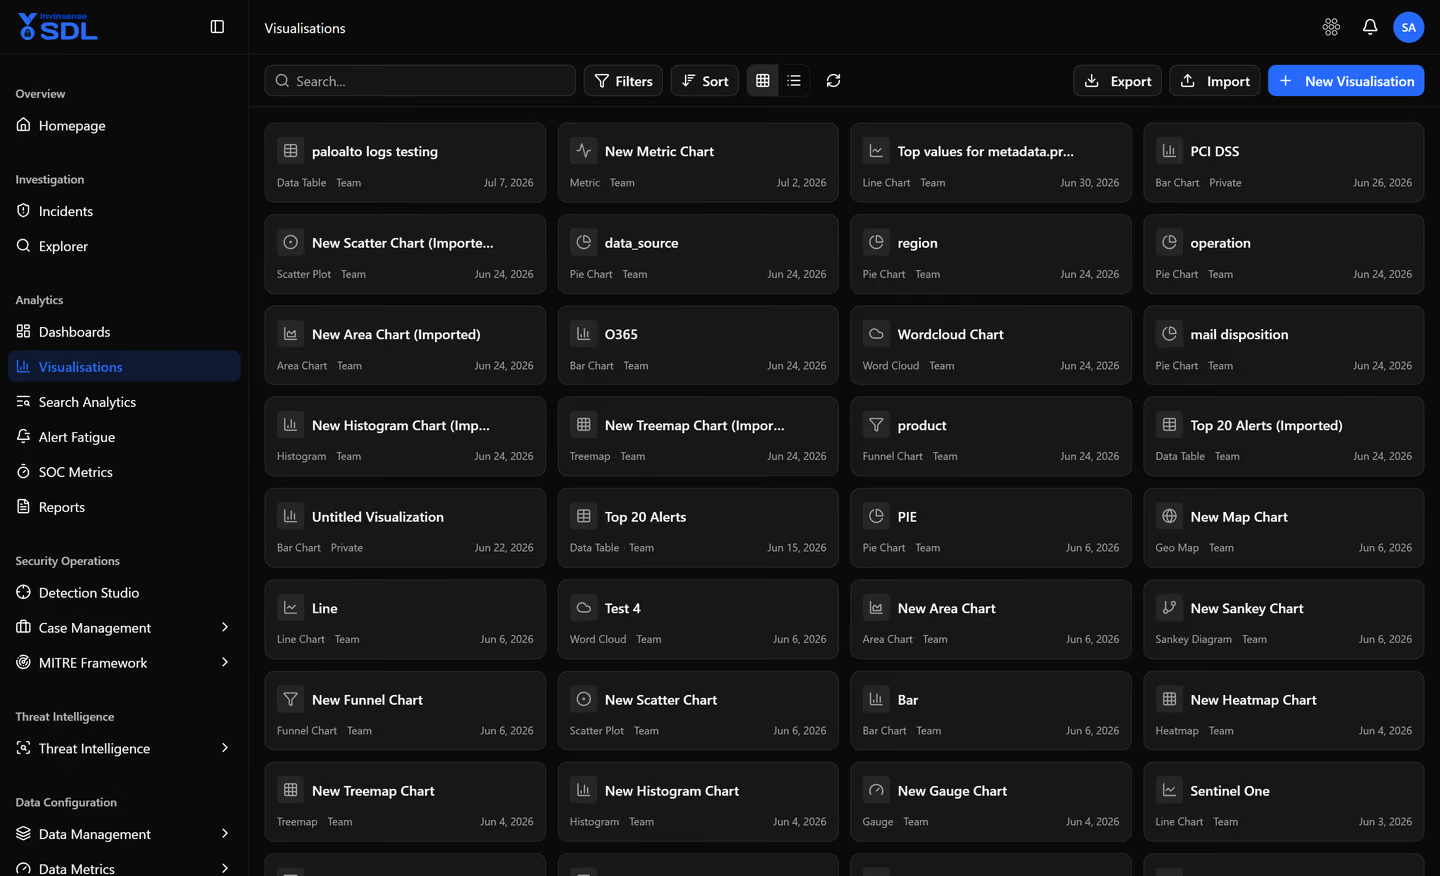
Part of Invinsense ISOC, the module acts as a centralized intelligence hub, seamlessly ingesting log data from diverse sources into a unified detection pipeline, with built-in OCSF normalization. Its Detection Studio aligns active correlation rules directly with the MITRE frameworks for tactical coverage. Customizable visual analytics dashboards with automated case management mappings streamline daily SecOps and drive incident response. Regiment AI powered intuitive conversational assistant summarizes critical case activities and simplifies complex investigations.
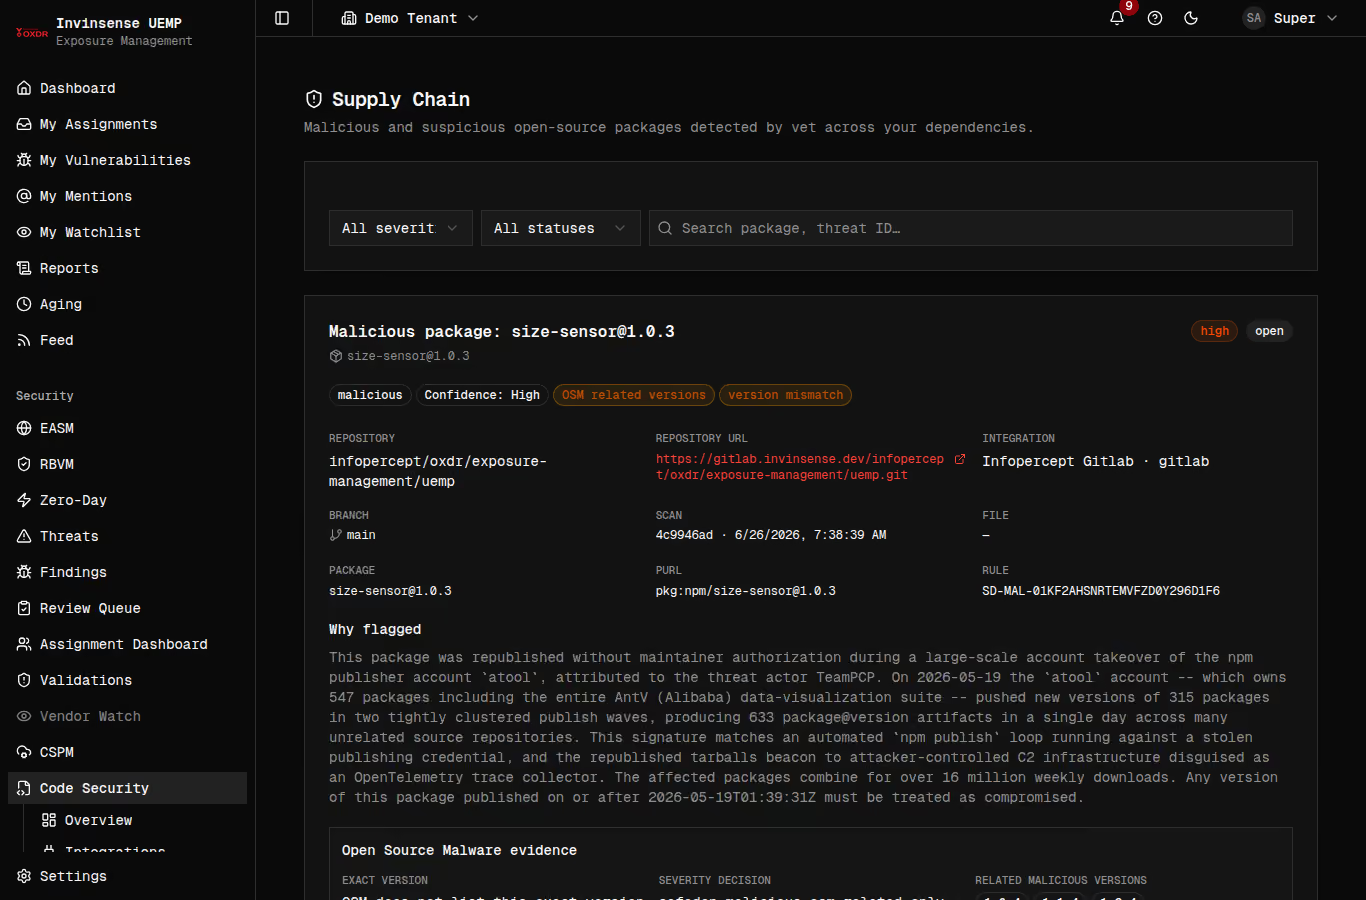
This module provides a sophisticated Application Security architecture designed to safeguard the modern software development lifecycle from code to production. Combining SAST, SCA, and container scanning, it performs multi-dimensional analysis to uncover critical code vulns and leaked secrets. Beyond standard static checks, it delivers visibility into complex software supply chain risks by generating dynamic SBOMs and proactively finds malicious open-source packages. Interactive findings and assignment dashboards help DevSecOps teams prioritize workloads and remediate architectural weaknesses before deployment.
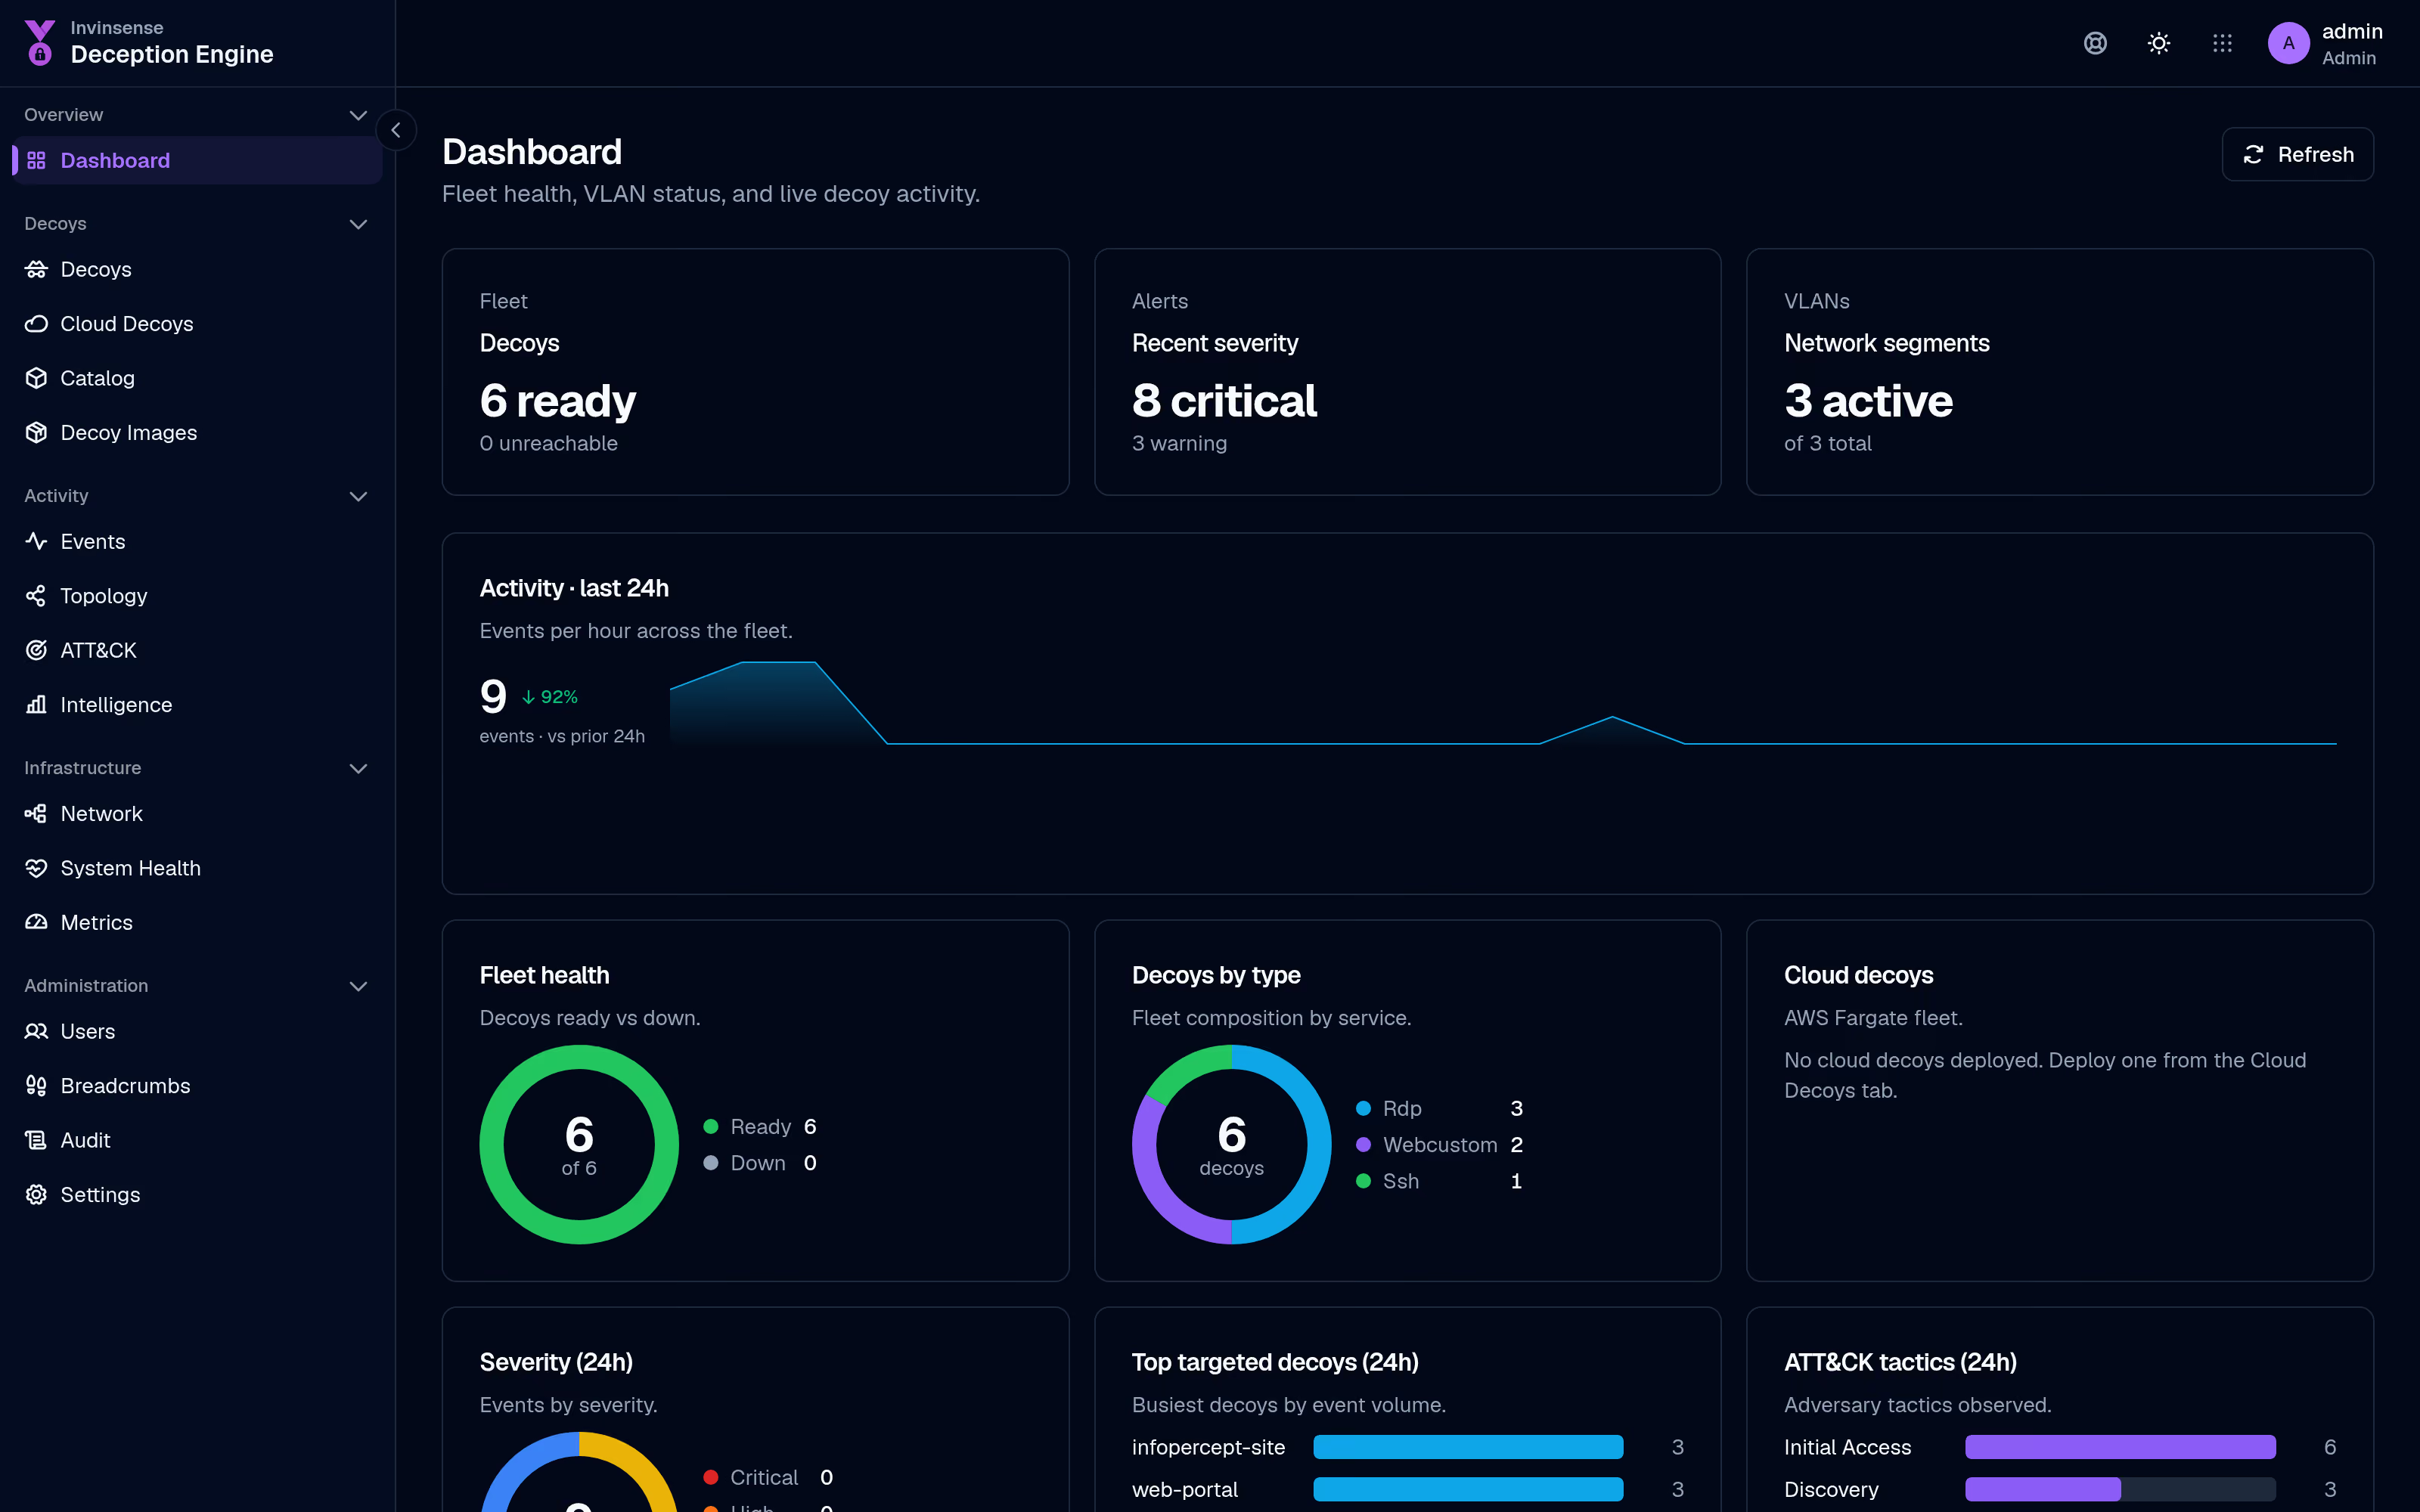
The module combines advanced deception and Automated Moving Target Defense (AMTD) capabilities to keep evolving adversaries at bay. This is done by dynamically detecting lateral movement, sophisticated network penetration and other evasive techniques, ensuring an organization's crown jewels are hidden, protected and remain uncompromised. Invinsense’ AMTD is a high-accuracy and innovative technology recognized by Gartner for enabling a shift from an ineffective “detect and respond” model to a "pre-emptive defense” approach. It capably complicates modern attackers’ and ransomware actors’ tactics to exploit the ever-expanding attack surface, discover and target vulnerabilities within the enterprise network.
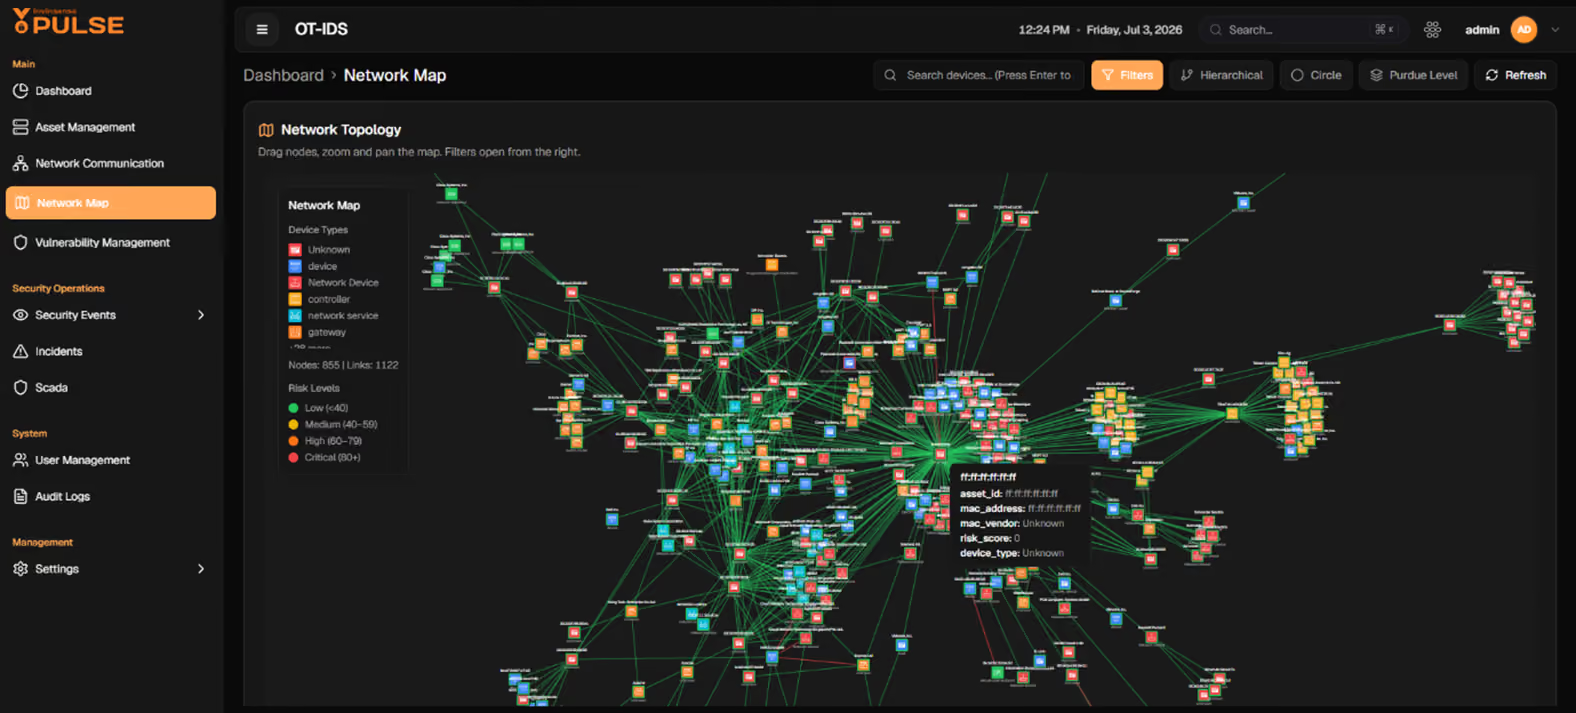
Result of a successful research productization, Invinsense OT and IoT security module provides a specialized cybersecurity capability, which is designed to safeguard industrial and critical infrastructure systems by continuously monitoring and detecting intrusions that are specifically targeted at OT and IoT landscapes. The technology plays a crucial role in maintaining the reliability and security of essential operations in sectors such as power & utility, oil & energy, manufacturing, automobiles, pharmaceuticals and transportation.
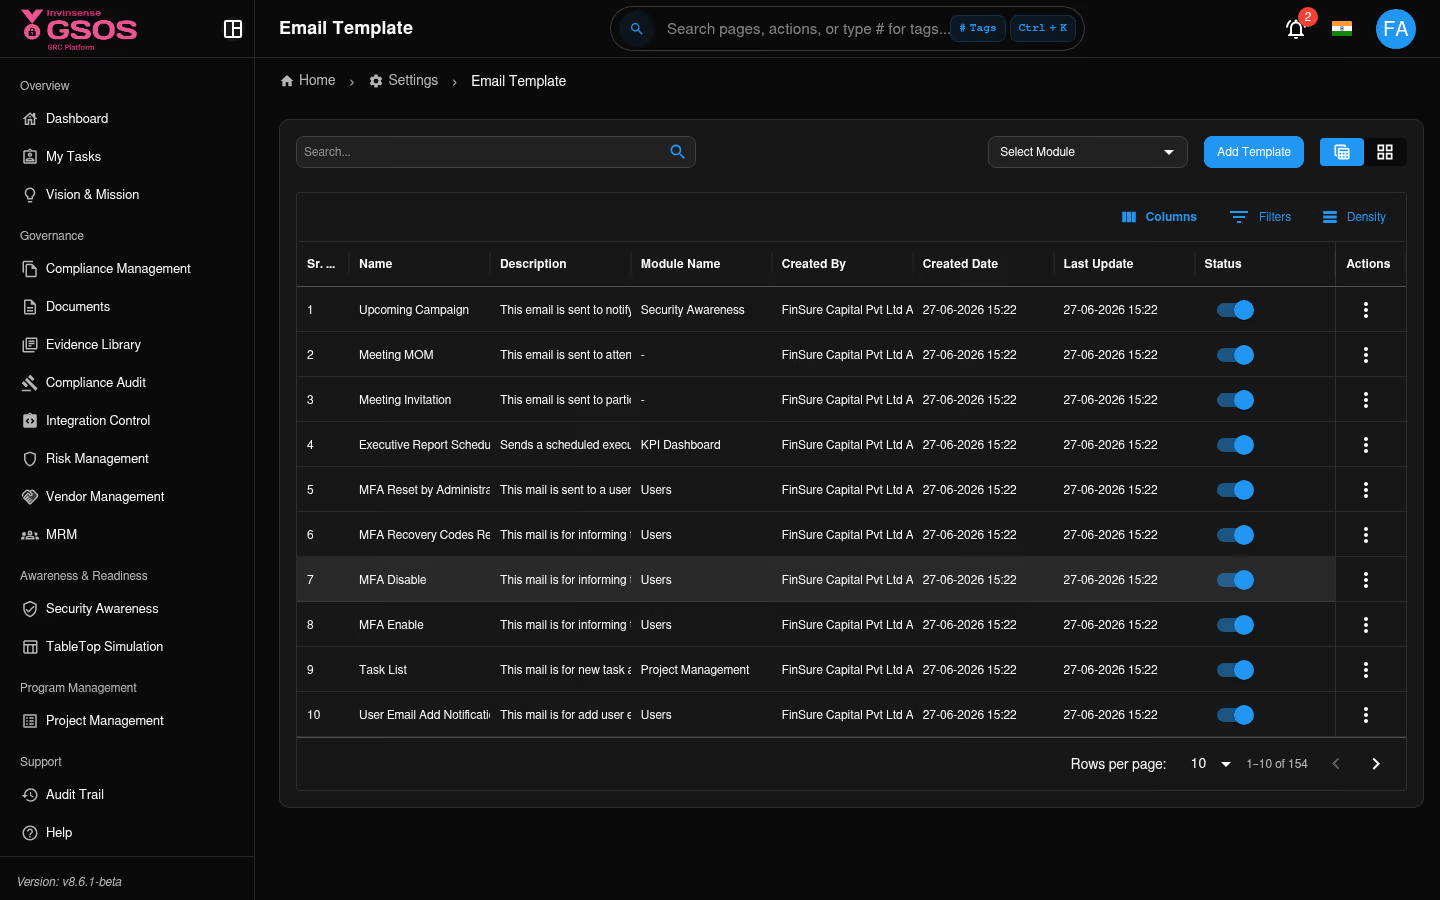
The module provides an intuitive solution for managing governance, risk and compliance (GRC) concerns and tasks. A wide range of built-in and pre-defined templates enable security teams to create policy documents and simulated test exercises on the fly, while letting them streamline workflows with consistency and accuracy. It assists in creating acybersecurity strategy, streamlining compliance management, enhancing security posture, reducing risks, increasing cybersecurity awareness and preparedness, and enabling organizations to meet regulatory requirements and safeguard sensitive & regulatory compliant data.
Discover complete cybersecurity expertise you can trust and prove you made the right choice!