

Modern SOCs Need More Than Visibility. They Need Context, Behaviour, and Deception.
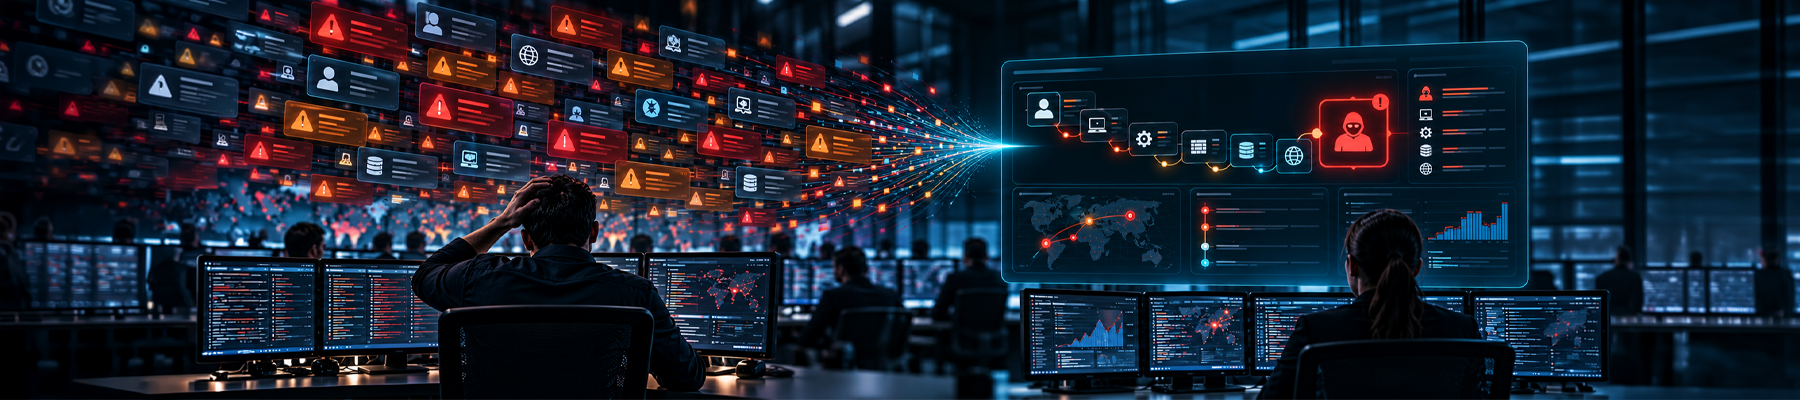
For years, security monitoring has followed a familiar model: Collect logs 🡪 Build detections 🡪 Generate alerts 🡪 Investigate incidents.
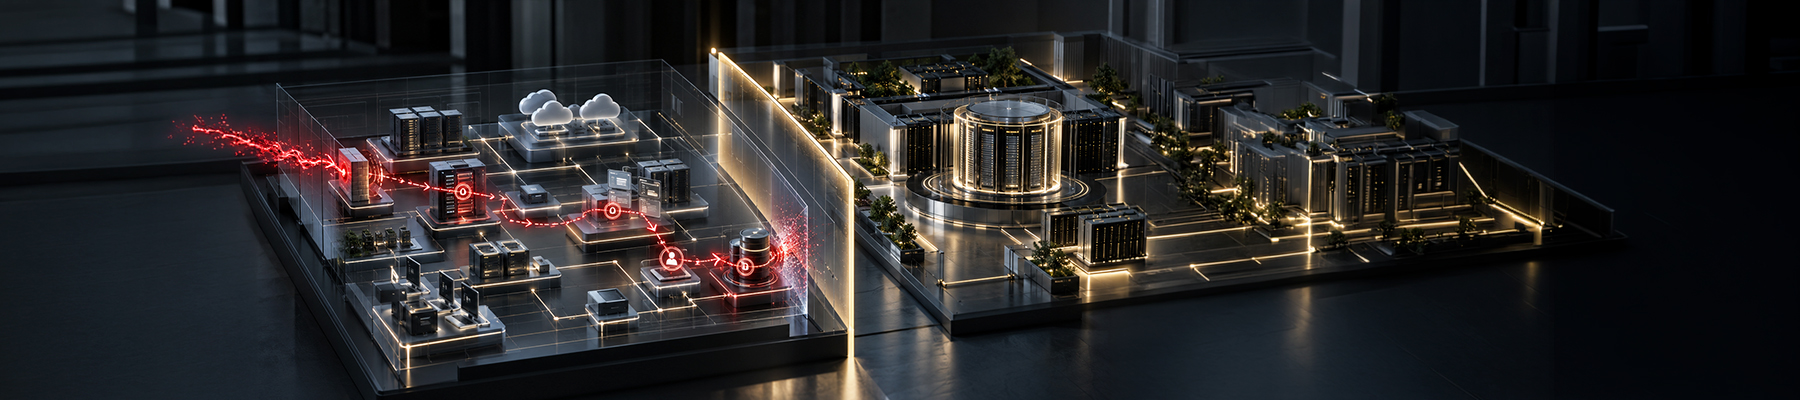
But attackers don't operate inside individual log sources. They move across identities, endpoints, networks, applications and cloud environments.
That creates a fundamental challenge for the SOC: How do you understand the attacker's journey, rather than simply react to individual events?
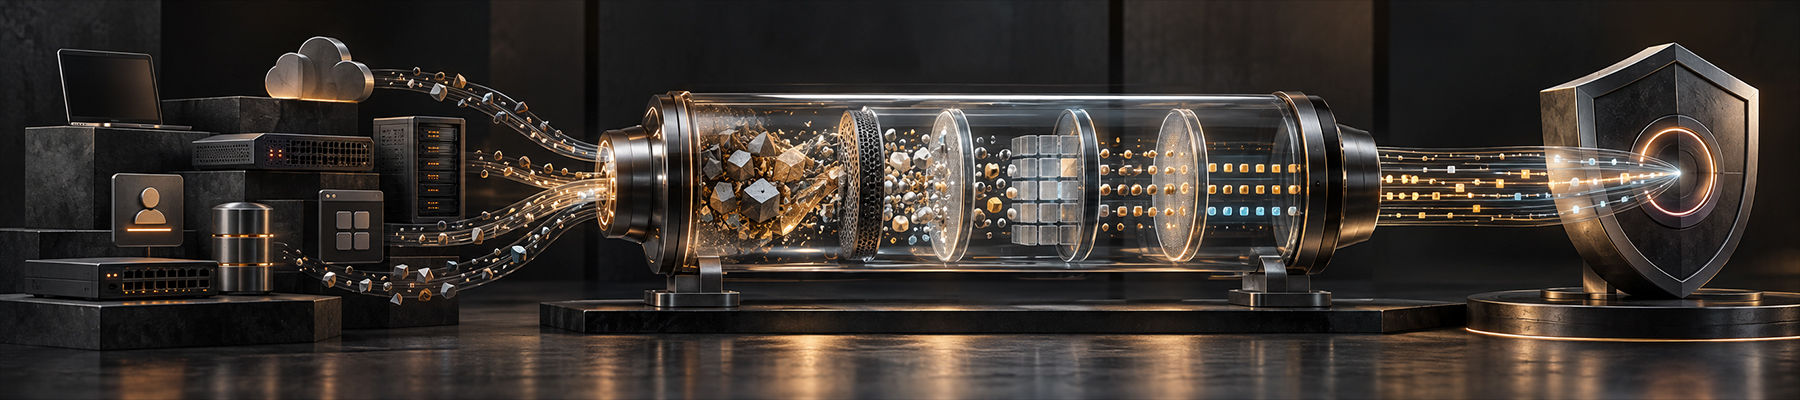
This is where three capabilities become powerful when brought together: Security Data Lake. NDR. Deception.
Each sees a different part of the attack. Therefore, they can create a much richer picture together.
The first requirement is a common security data foundation.
Without it, the SOC sees fragments.
Individually, these may not mean much. But together, they may describe an attack.
Invinsense Security Data Lake provides a common foundation by ingesting, parsing, enriching and normalizing security data into OCSF 1.9.0. Its streaming correlation engine can then correlate activity across different sources and detection patterns.
The value isn't simply collecting more data. But to turn scattered security events into security context.
The NDR adds another dimension here. Endpoint telemetry tells us what happened on a device.
NDR helps the SOC understand what is happening between devices.
Now the SOC isn't looking at an isolated endpoint alert.
It can start asking:
Therefore this context significantly changes the investigation.
What if we could create assets that are designed to attract and observe attackers?
That's the role of Deception.
Instead of waiting for an attacker to compromise a production system, deception introduces controlled assets, identities or services that should not normally attract legitimate user activity.
So when something interacts with them, the signal itself becomes meaningful.
There shouldn't be a legitimate reason for an employee to access a decoy administrative service.
There shouldn't be a legitimate reason for an attacker to enumerate a decoy asset.
Therefore SOC gets something extremely valuable: high-context behavioral signals.
This is where the architecture becomes interesting.
Imagine an attacker compromises an endpoint.
Security Data Lake provides a broader context. NDR observes unusual network behavior and movement. Deception creates a high-confidence signal when the attacker interacts with a decoy.
Instead of three disconnected alerts, the SOC can potentially build a story: Initial compromise → Discovery → Network movement → Deception interaction → Detection → Investigation → Response
That is a very different SOC experience.
The question is no longer: "Which alert should the analyst investigate?"
It becomes: "What is the attacker trying to accomplish?"
A data lake alone doesn't tell you everything.
NDR alone doesn't provide the complete investigation context.
Deception alone only tells you when something interacts with the trap.
The value comes from connecting these signals.
Invinsense brings these capabilities into the same security operations ecosystem, allowing security teams to combine security telemetry, network behavior and deception signals rather than investigate them as separate security products.
That matters because security teams don't need another collection of dashboards.
They need a connected view of the attack.
The future SOC won't simply be about collecting more telemetry.
It will combine different forms of visibility.
Security Data Lake
→ What is happening across the environment?
NDR
→ How is the attacker moving and communicating?
Deception
→ Where is the attacker interacting with something they shouldn't?
Detection & Response
→ What should the SOC do about it?
And the loop can continue through validation and improvement.
Discover → Detect → Deceive → Investigate → Respond → Validate → Improve
That is the real opportunity. Not just detecting an attack.
Understanding the attacker's behavior before they can turn that behavior into business impact.
The question for the modern SOC:
Don't just ask: "How many threats can we detect?"
Ask: "How much of the attacker's journey can we see, understand and validate?"
Because the strongest SOC isn't the one with the most alerts.
It's the one that gives analysts enough context to understand what the attacker is actually doing.
Discover complete cybersecurity expertise you can trust and prove you made the right choice!