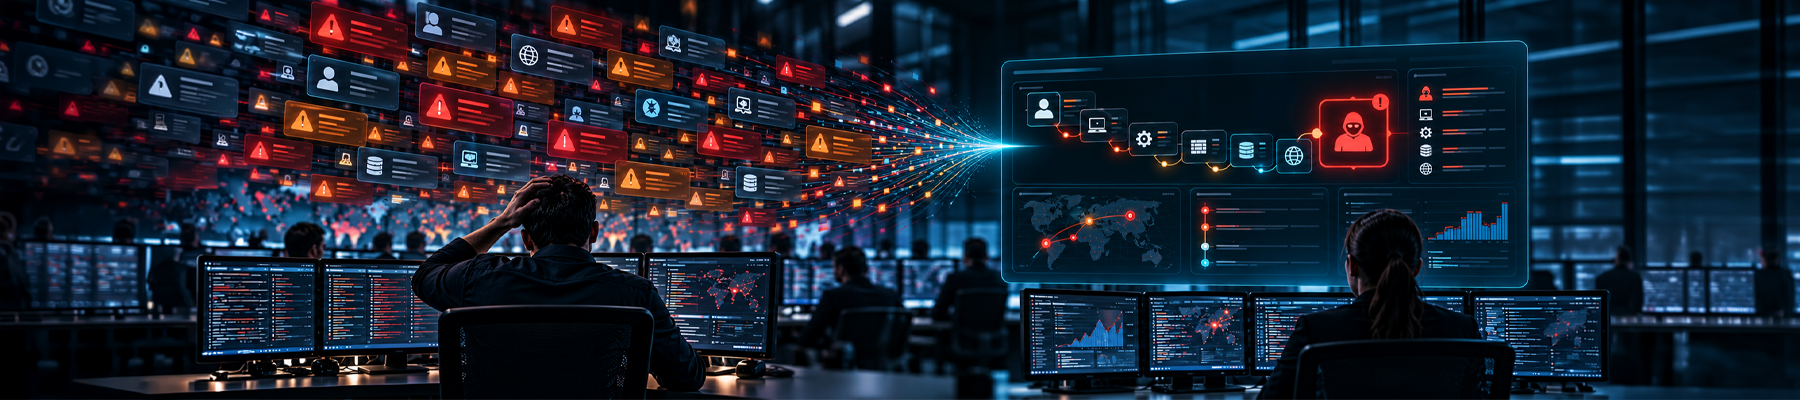


Every SOC has an alert problem. There are too many alerts. Some are duplicates. Some are benign. Some are low priority. Some contain useful information but lack enough context for an analyst to act on them quickly.
So the natural response is: “Reduce the alerts,
But there is a risk. What if, in trying to reduce alert volume, we reduce visibility instead?
Consider these events:
Individually, some of these events may not justify an investigation. But together, they could describe an attack.
If each event becomes a separate alert, the SOC gets noise. If some are simply suppressed, the SOC may miss the bigger picture.
Therefore the real challenge is not: “How do we generate fewer alerts?”
It is: “How do we turn many signals into fewer, more meaningful security decisions?”
This is where security correlation becomes important. A modern SOC should be able to recognize relationships between events rather than treating every event independently.
Invinsense Security Data Lake provides a dedicated streaming correlation engine that evaluates events as they move through the pipeline. It supports multiple detection approaches, including sequence detection, risk scoring, beaconing, diversity, and meta-alert correlation.
Therefore, this allows the SOC to connect seemingly unrelated signals.
For example: Failed authentication à Successful authentication à New endpoint access à Suspicious process à Malicious network connection.
Instead of creating five disconnected investigations, the SOC can recognize the possibility of one developing attack. That's the difference between alert correlation and security understanding.
Another problem with traditional alerting is that signals are often treated too independently.
But the risk keeps accumulating.
One suspicious event may be low risk. But several related events involving the same user, endpoint, or identity may represent something much more serious.
Risk-based detection allows the SOC to consider that accumulation.
Invinsense supports risk-score detection alongside threshold, sequence, N-of-M, and other detection types.
This changes the analyst's experience.
Instead of asking: "Which alert should I open next?”
The SOC can focus on: “Which activity represents the greatest potential risk?”
Correlation alone isn't enough. The SOC also needs context.
A suspicious process on a standard workstation is one thing. But the same activity on a critical server used by a privileged administrator is something else.
Threat intelligence can add another layer. Is the destination IP known to be malicious? Has this indicator appeared elsewhere? Has the same behavior occurred previously?
Invinsense combines security telemetry with context such as threat intelligence, asset and identity information, enabling investigations to move beyond the individual alert.
The result is a better question. Not “Is this alert suspicious?”
but: “How important is this activity in the context of our environment?”
There will always be alerts that don't deserve analyst attention.
Suppression has a place. But that suppression should be informed by evidence.
Which detections are consistently noisy? Which alerts are duplicates? Which conditions can safely be suppressed? Which detections are producing useful signals but lack appropriate thresholds or correlation?
Invinsense includes alert grouping, suppression controls, and alert-fatigue analysis to help identify noisy detections and manage them systematically.
The objective isn't to make the dashboard look quieter. But to make the analyst's attention more valuable.
The best outcome isn't simply a better alert. But a faster path from signal to action.
When a meaningful security event is identified, it should naturally move into investigation and response.
Invinsense connects alerts with case management, including alert-to-case automation, investigation timelines, IOC tracking, related alerts, tasks, attack graphs, and SLA tracking.
That creates a cleaner operational flow: Signals → Correlation → Prioritization → Investigation → Response.
Instead of: Signals → More alerts → Manual sorting → Tool switching → Investigation.
The same philosophy can extend beyond the SOC.
Offensive security can help identify which attack behaviors deserve priority. Defensive security can determine whether those behaviors can be detected and correlated. Compliance and risk can help determine which controls and business assets require the greatest attention.
This creates a useful feedback loop: Risk → Attack Scenario → Security Signals → Detection → Response → Control Validation.
Alert management then becomes more than a SOC efficiency exercise.
It becomes part of the organization's broader risk-management strategy.
A quiet SOC isn't necessarily a secure SOC. An empty alert queue could mean excellent detection engineering. But it could also mean aggressive suppression.
The real measure is different: Are analysts spending their time on the events that matter most?
That's where modern SOC architecture needs to evolve. The objective shouldn't be to eliminate alerts. But to eliminate meaningless decisions.
Because when six weak signals can be connected into one high-confidence investigation, the SOC doesn't necessarily need less data.
It needs better intelligence from the data it already has.
And that is the real purpose of reducing alert fatigue: Not fewer alerts, but better decisions.
Discover complete cybersecurity expertise you can trust and prove you made the right choice!