

SOC teams spend enormous effort building detection rules. They tune thresholds. Map techniques to MITRE ATT&CK. Reduce false positives. Test attack scenarios.
But there is a question that often gets less attention: Can you trust the data reaching your detection engine?
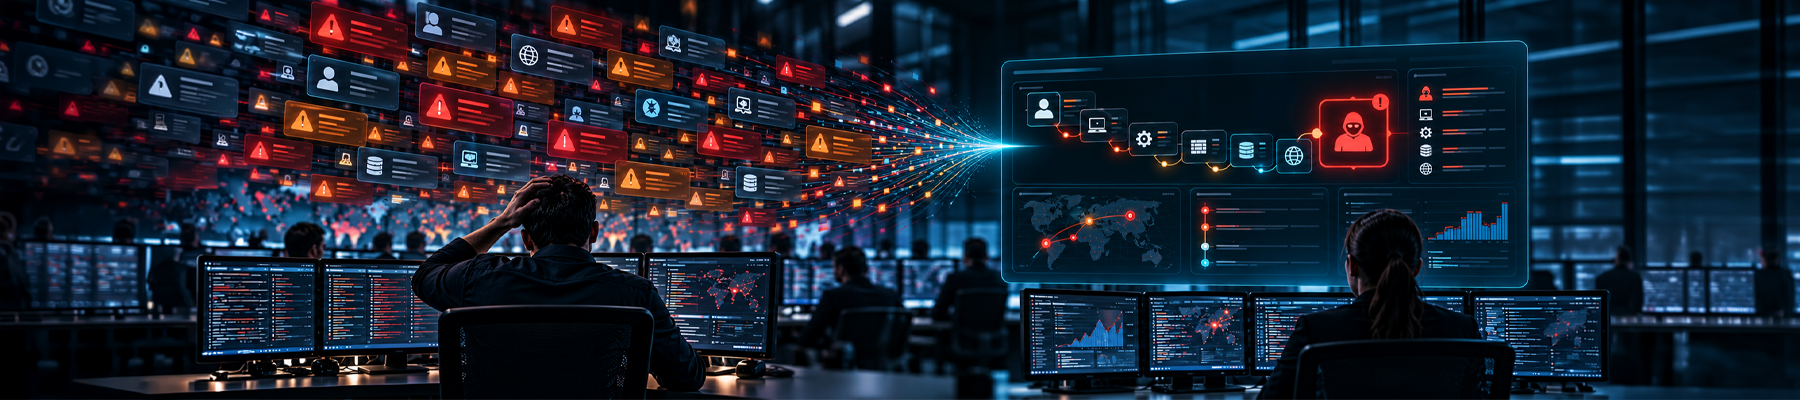
Because when the data pipeline breaks, detection breaks with it. A firewall changes its log format. A SaaS platform adds a new field. An endpoint stops sending telemetry. A parser fails. A critical field is mapped incorrectly. The detection rule may still be active. The dashboard may still look normal. But your security control may already be blind.
Detection Starts With Data Quality
Consider a simple attack scenario. An endpoint executes PowerShell, establishes persistence, and then connects to an external malicious IP.
Your SOC has a detection designed to identify this sequence.
But what if:
The detection logic hasn't changed. Its ability to detect the attack has. That is why the security data pipeline should not be treated as plumbing. It is part of the security control.
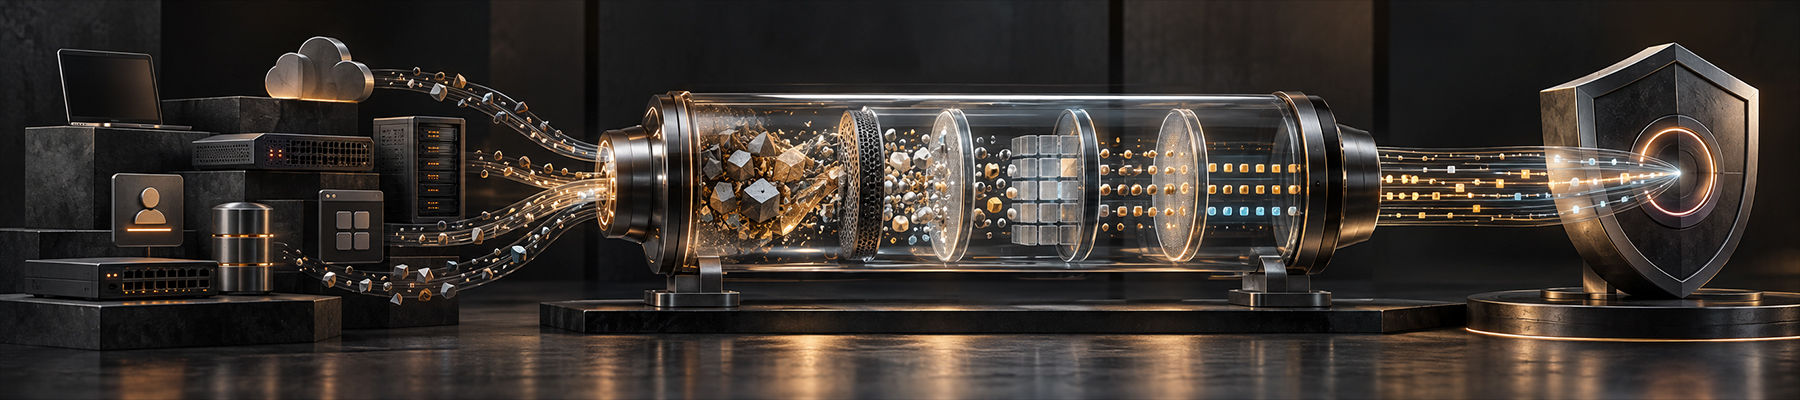
Invinsense Security Data Lake is designed around the idea that security data must be usable, consistent, and continuously trustworthy before it can support detection.
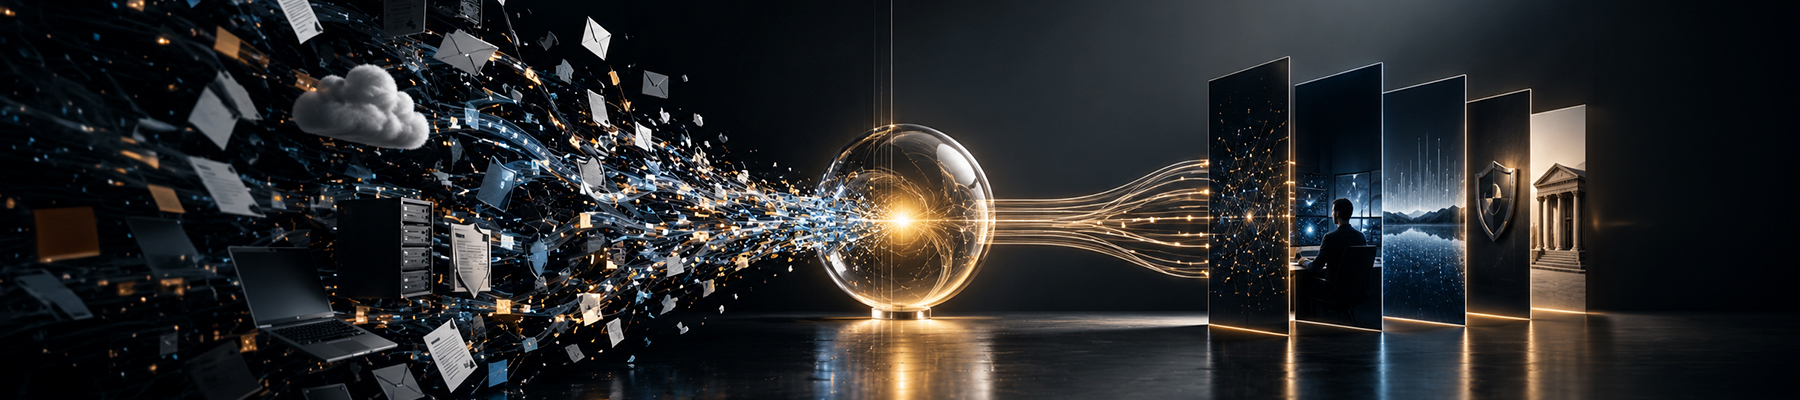
Data is ingested, parsed, enriched, and normalized into OCSF 1.9.0, creating a common security data foundation across different sources. Invinsense supports all 87 OCSF event classes.
But normalization alone isn't enough.
Security environments change constantly.
That is why Invinsense includes an Agentic Parser Generator (Autoparser) that can create and validate parsers when new log formats, schema changes, or parsing issues appear. Parsers pass multiple validation gates, including OCSF conformance, required-field coverage, and performance checks, before being deployed.
This is an important shift.
Instead of treating parser maintenance as a manual SOC task, Invinsense makes the security data pipeline an active part of the security architecture.
That distinction matters.
Traditional monitoring often asks: Is the source sending data?
A security operations platform needs to ask much more: Is the data being parsed? Is it normalized correctly? Are the fields required by our detections present? Can our correlation engine use it? Can we investigate the resulting events later?
Invinsense connects these layers. Its streaming correlation engine operates on normalized security data and supports pattern, sequence, threshold, risk-score, and other detection models. It also provides detection testing and Retro Scan capabilities to validate detection logic against historical data.
So the pipeline isn't disconnected from detection. The data foundation, detection engine, and investigation layer work as one security workflow.
A security data pipeline should not exist in isolation.
An attack simulation can tell you what telemetry a real attack generates.
The defensive layer can determine whether that telemetry produces a detection.
Case management can track what happened and how it was handled.
Compliance can provide evidence that the required control operated.
And historical data can be used to validate whether the same detection would have identified earlier activity.
This creates a continuous loop: Attack → Telemetry → Detect → Respond → Validate → Improve
Instead of treating offensive security, defensive security, and compliance as separate activities, Invinsense connects them around the same security data and operational context.
Don't just ask: "Do we have a detection for this threat?"
Ask: "Can we prove that the telemetry required to detect this threat is healthy, usable, and reaches the detection engine?"
That is a much stronger security question.
Because a detection that cannot reliably see the attack is not really a security control.
Invinsense turns the security data pipeline from invisible plumbing into an observable, validated foundation for security operations.
And that is where reliable detection begins.
Discover complete cybersecurity expertise you can trust and prove you made the right choice!