

At 2:17 AM, a critical alert appears in the SOC. A suspicious PowerShell process has been detected on an endpoint.
The analyst has one simple question: What actually happened?
That question often starts a familiar journey:
The SOC may have detected the event quickly. But the investigation was slow. And that distinction matters.
Security teams have become very good at collecting data. Endpoints generate telemetry. Networks generate events. Identity systems generate authentication records. Cloud platforms generate activity logs. Threat intelligence generates indicators.
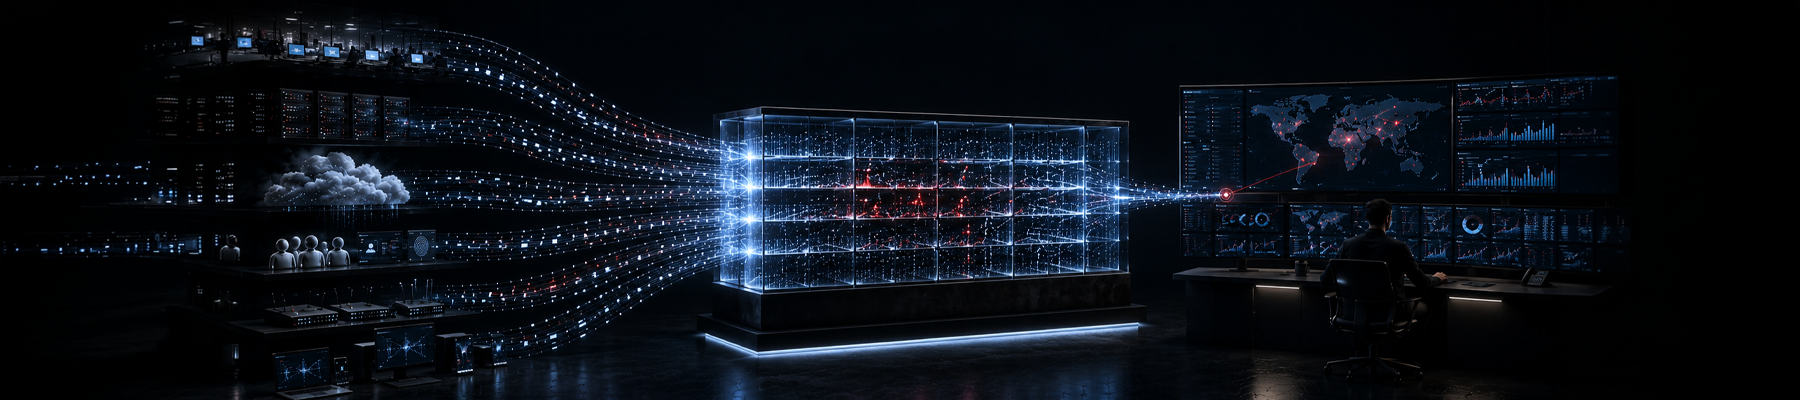
But the problem is that the visibility is fragmented. An endpoint alert lives in one system. Network activity lives somewhere else. Threat intelligence has another interface. Vulnerability information is managed separately. Case management is somewhere else again. And the analyst becomes the integration layer.
Therefore, it creates a hidden operational cost: context switching.
Consider a suspicious PowerShell alert. On its own, it is simply a signal.
But now add context to it:
The original alert hasn't changed. But the context has changed.
The context turns from:
“Something suspicious happened.”
into:
“We may be looking at an active attack.”
Therefore, the unit of work in a modern SOC should not be an alert. It should be the investigation.
This is where the architecture behind Invinsense becomes important.
Invinsense Security Data Lake brings ingestion, normalization, enrichment, detection, investigation, and retention into a common security-data foundation. Security events are normalized to OCSF 1.9.0, thereby allowing data from different sources to be analyzed using a consistent model.
For an analyst, that means something simple: Endpoint, identity, cloud, and network events can become part of the same investigation.
The objective isn't to collect more data, but to make existing data more usable.
Traditional correlation often asks: “Did Event A and Event B happen?”
But modern security operations need to ask: “What story do these events tell together?”
Invinsense SDL's streaming correlation engine evaluates events as they move through the pipeline and supports multiple detection models, including sequence detection, risk scoring, beaconing, diversity, and meta-alert correlation.
Therefore, weak signals become meaningful when viewed together:
Individually, they may not mean much. But together, they may describe an attack.
Good investigations naturally move through questions: What happened? → Who was involved? → What happened next? → Has this happened elsewhere? → Is the activity malicious? → How far has it spread? → What should we do now?
Invinsense provides IQL for security-focused search and analytics, alongside investigation capabilities such as entity graphs, timelines, field statistics, and an investigation workbench.
Therefore, the goal is straightforward: Reduce the number of steps between a question and an answer.
Sometimes the most important evidence isn't from the last hour. But from six months ago. An attacker may have entered the environment long before the SOC recognized the compromise. A domain may only become known as malicious today. A new detection may reveal activity that previously looked harmless.
Therefore, security retention is not simply a storage decision. It is an investigative capability.
Invinsense SDL combines a Lakehouse for hot analytics with cold storage for long-term retention and supports retention of raw security logs. It also provides Retro Scan and threat-intelligence Retro Hunting to apply new detection or intelligence to historical data.
In other words: Today's knowledge can be used to investigate yesterday's activity.
There is another opportunity here. Instead of manually performing every search, an analyst can ask questions in natural language. Regiment AI can translate those questions into IQL, search events and alerts, summarize incidents and timelines, explain detections and suggest investigative pivots.;
Therefore the goal isn't to remove the analyst from the process. But to remove repetitive work.
The analyst still validates the evidence, challenges the hypothesis and makes the security decision. AI simply helps shorten the path to that decision.
Investigation becomes even more valuable when it connects to the broader security lifecycle. An offensive assessment can demonstrate how an attacker might move through the environment.
The defensive team can then ask:
And compliance can ask:
This creates a continuous loop: Attack → Telemetry → Detection → Investigation → Response → Evidence → Improvement.
Therefore, instead of having separate offensive, defensive, and compliance activities, the organization gets one connected security process.
We often ask how quickly a SOC can detect an event. But we should also ask: How quickly can an analyst understand it well enough to make the right decision?
Because processing alerts isn't the objective. Making Good decisions is the core objective. Therefore it requires:
And the integration of Offensive, Defensive, and Compliance capabilities closes the loop.
Ultimately, a SOC isn't successful because an alert appears in seconds. It is successful when the analyst can quickly answer: What happened? How serious is it? How far has it gone? And what should we do now? That isn't just detection speed, but also investigative speed.
Discover complete cybersecurity expertise you can trust and prove you made the right choice!